Evidence-backed scam triage in one click
Open-source analyzer for suspicious emails, texts, URLs, and phone numbers. Paste it, run analysis, get a verdict built from evidence. An unknown is never marked safe.
What it does
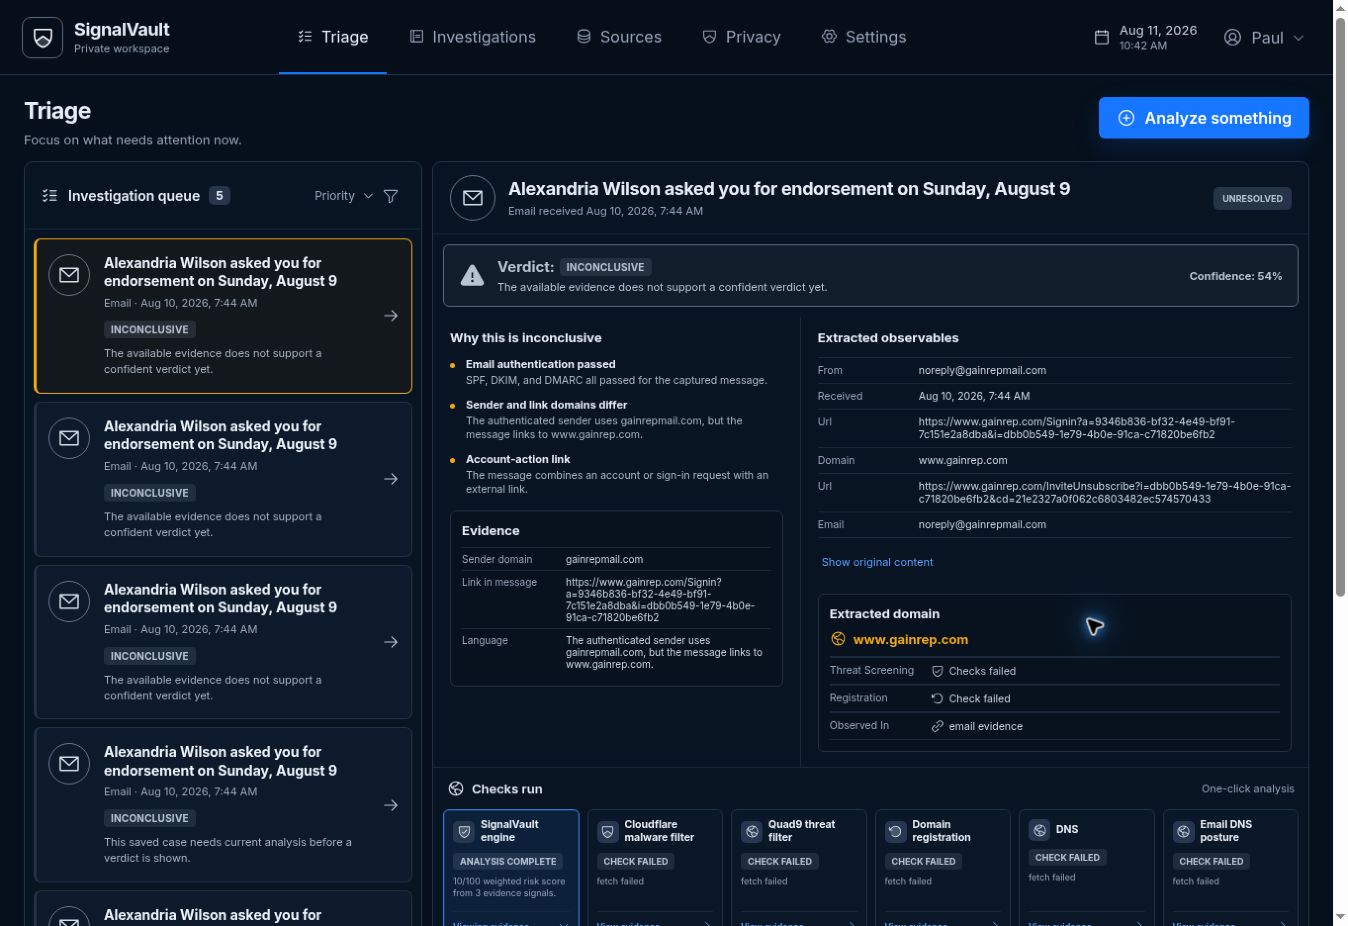
Header forensics
RFC 822 parsing with folded headers, SPF / DKIM / DMARC result analysis, and sender vs Reply-To comparison.
URL & sender intel
Direct-IP, punycode, shortener, user-info, suspicious-TLD and lookalike detection across extracted URLs, domains, emails, and phone numbers.
Threat-feed screening
Cloudflare malware and phishing DNS checks, Quad9 threat blocking, RDAP domain age, plus optional VirusTotal, Web Risk, and AbuseIPDB.
Honest risk scoring
Urgency, credential, payment, and irreversible-payment scoring. Verdict aggregation never turns an unknown into safe.
Zero-config triage
Regex detectors, extraction, and lookalike checks run right in the browser with no accounts or API keys.
Owner-scoped storage
Reports saved to a private workspace with row-level security, or kept locally in your browser.
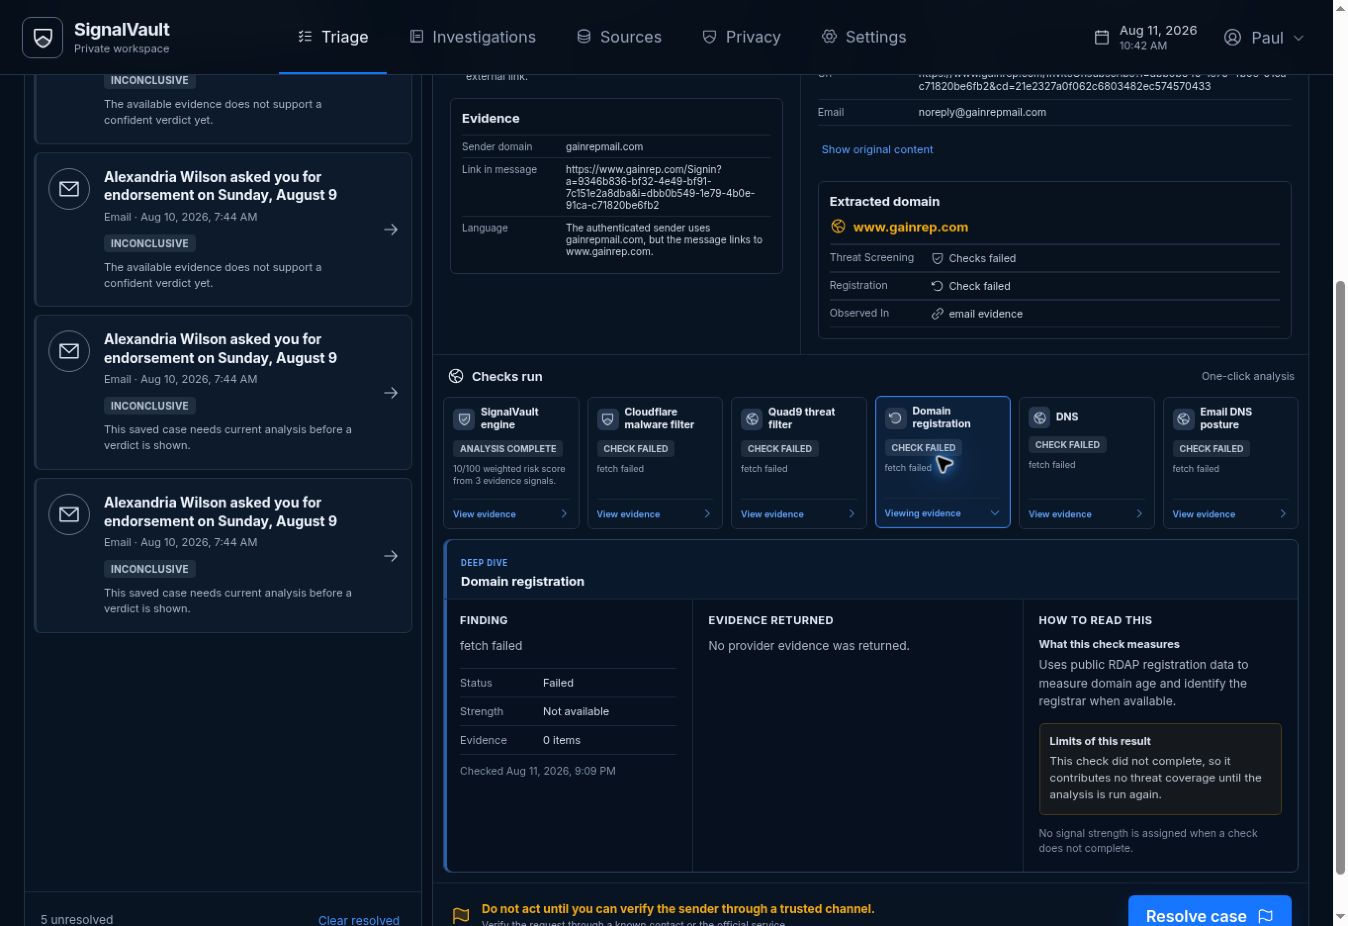
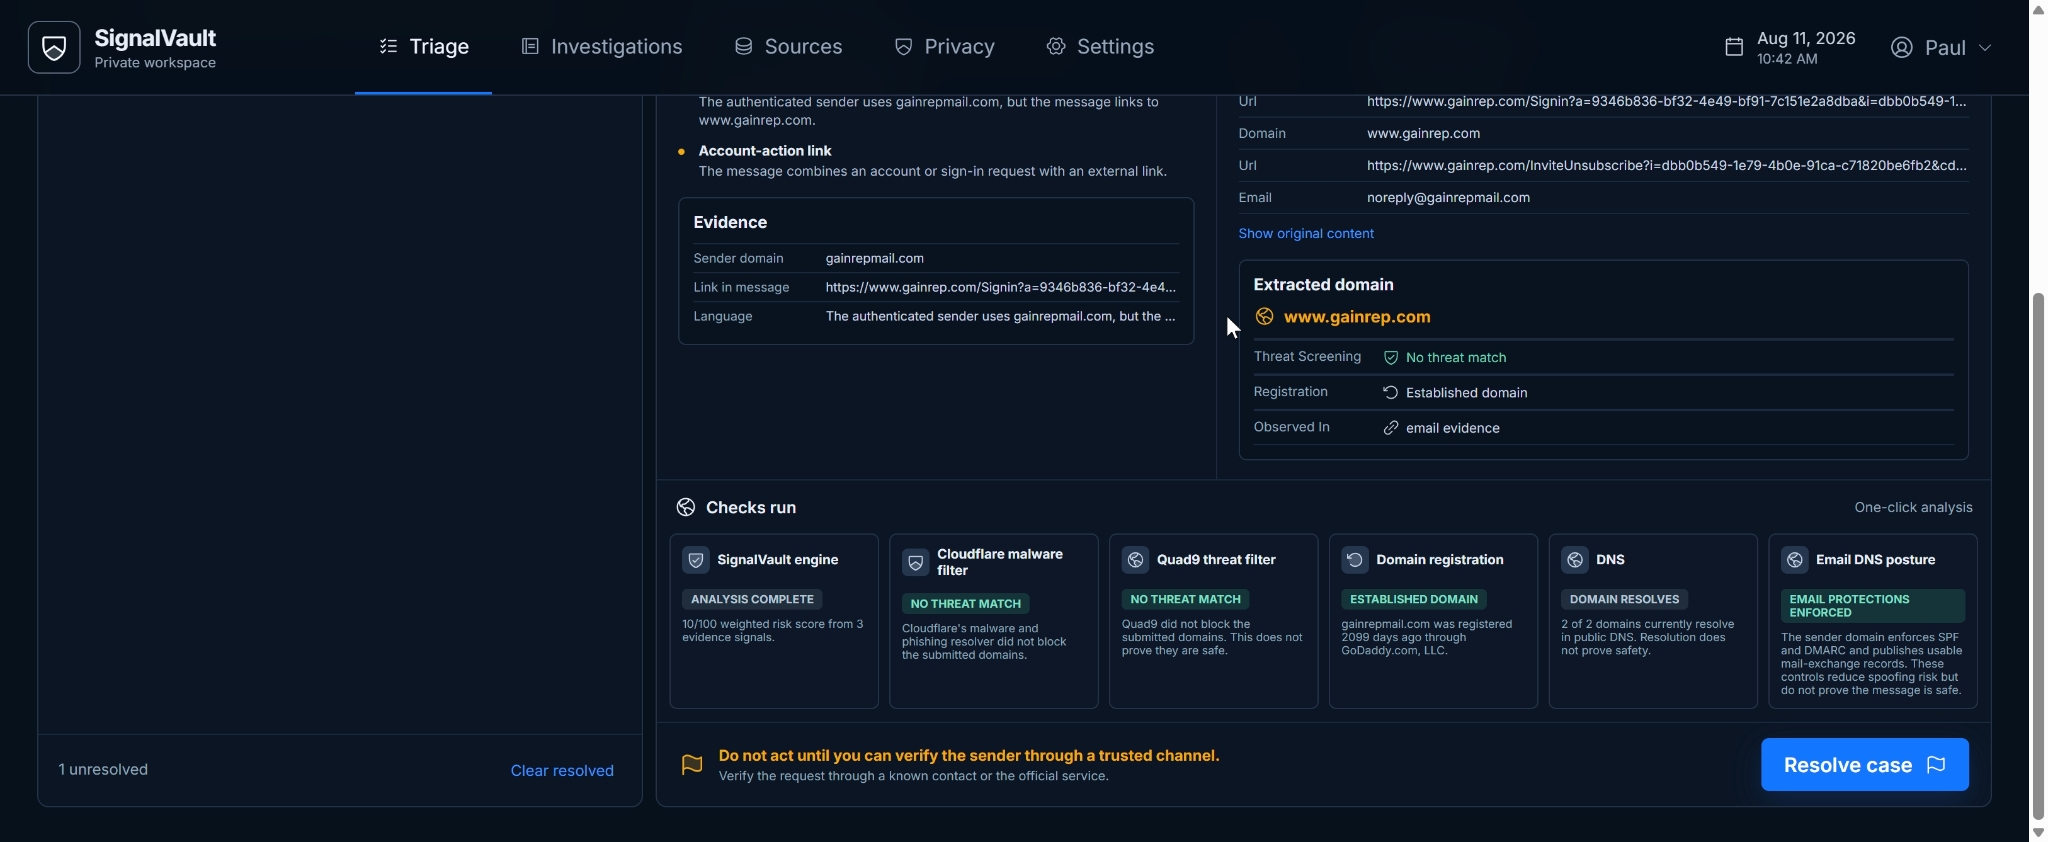
Screens
Get started
- Clone the repo.
git clone https://github.com/p-romeo/signal-vault - Install and run.
npm install && npm run dev(Node.js 22+) - Optionally add keys. Google Web Risk, VirusTotal, or AbuseIPDB keys go in
.dev.varsfor deeper reputation checks. - Analyze. Paste any email, URL, SMS, or phone number and hit Run one-click analysis.
Triage decisions deserve evidence, not gut feelings.
SignalVault supports decisions but never guarantees something is safe — failed or missing provider results stay explicit. The worker never visits submitted destinations, and evidence stays in your own workspace.